> ## Documentation Index
> Fetch the complete documentation index at: https://docs.leen.dev/llms.txt
> Use this file to discover all available pages before exploring further.
# Microsoft Entra Instructions
> Instructions on how to onboard a Microsoft Entra Integration
## Required Permissions
The user authorizing the Microsoft Entra connection must be able to **grant tenant-wide admin consent for Microsoft Graph permissions**.
### Admin Consent Requirement
This integration uses the `/adminconsent` endpoint with **Microsoft Graph API** permissions, which requires admin consent to authorize the application on behalf of the entire organization.
**Important:** This integration requires **Microsoft Graph app roles (application permissions)**. Only **Privileged Role Administrator** or **Global Administrator** can grant admin consent for Microsoft Graph application permissions. Cloud Application Administrator and Application Administrator roles cannot grant consent for these permissions.
### Microsoft Graph Permissions Required
The Leen Microsoft Entra app requires the following **Microsoft Graph application permissions**:
* **User.Read.All**: Read user profiles
* **Group.Read.All**: Read group information
* **Application.Read.All**: Read application information
* **IdentityRiskyUser.Read.All**: Read identity risk information
* **IdentityRiskEvent.Read.All**: Read identity risk events
* **Policy.Read.All**: Read organization policies
* **Policy.Read.Authentication**: Read authentication policies
* **AuditLog.Read.All**: Read audit logs and sign-in logs
### Roles That Can Grant Admin Consent
**Privileged Role Administrator** (Recommended)
* Can grant consent for apps requesting **any permission, for any API**
* Can grant Microsoft Graph app roles (application permissions)
* No limitations on API types or permission scopes
* Full admin consent capabilities
**Global Administrator**
* Can grant consent for any application
* Can grant Microsoft Graph app roles (application permissions)
* Has full access to all administrative features
* Can grant admin consent without restrictions
**Cloud Application Administrator** ❌ (Not Sufficient)
* **Cannot** grant consent for Microsoft Graph app roles (application permissions)
* Cannot authorize this integration
**Application Administrator** ❌ (Not Sufficient)
* **Cannot** grant consent for Microsoft Graph app roles (application permissions)
* Cannot authorize this integration
### Which Role to Use
**Requirement:** You **must** use a **Privileged Role Administrator** or **Global Administrator** account for the authorization in step 2. Since this integration requires Microsoft Graph app roles (application permissions), Cloud Application Administrator and Application Administrator roles do not have sufficient permissions.
## Key Points
* Admin consent is required to grant Microsoft Graph application permissions
* The authorizing user **must** be a Privileged Role Administrator or Global Administrator
* Cloud Application Administrator and Application Administrator cannot grant these permissions
* Permissions must be explicitly granted even after application registration
* Admin consent must be re-granted if application permissions are changed
## Onboarding
Follow the steps below to onboard your environment to our Microsoft Defender app.
With your Leen API Key and your Customer's Org ID, make a API request to create a new Microsoft Defender Connection.
More information can be found on the [API Reference page.](/api-reference/provisioning/add-new-connection)
```json theme={null}
{
"vendor": "MS_ENTRA"
}
```
The response will look like this:
```json theme={null}
{
"id": "c54de187-df62-4e95-b10f-0ab53b095d9d",
"vendor": "MS_ENTRA",
"refresh_interval_secs": 14400,
"timeout_secs": 1800,
"organization_id": "fbd8b095-3c39-4137-9478-c32308444202",
"oauth2_authorize_url": "https://login.microsoftonline.com/common/adminconsent?....."
}
```
Open the `oauth2_authorize_url` from the previous step in a new tab.
This will prompt the admin user to authorize Leen's Microsoft Entra app to access their Microsoft Entra resources.
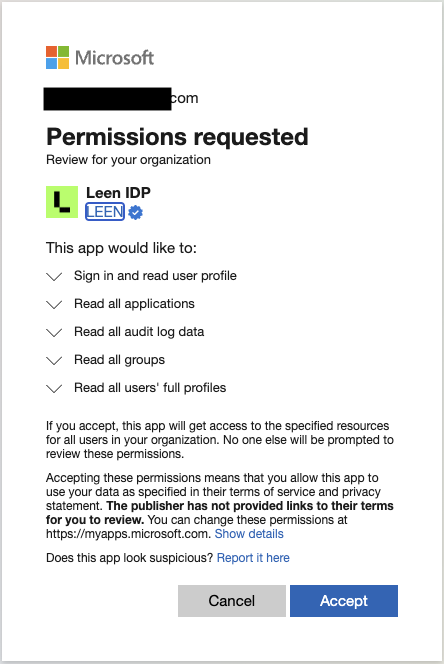 Once the user has authorized the app, they will be redirected to Leen on a successful authorization.
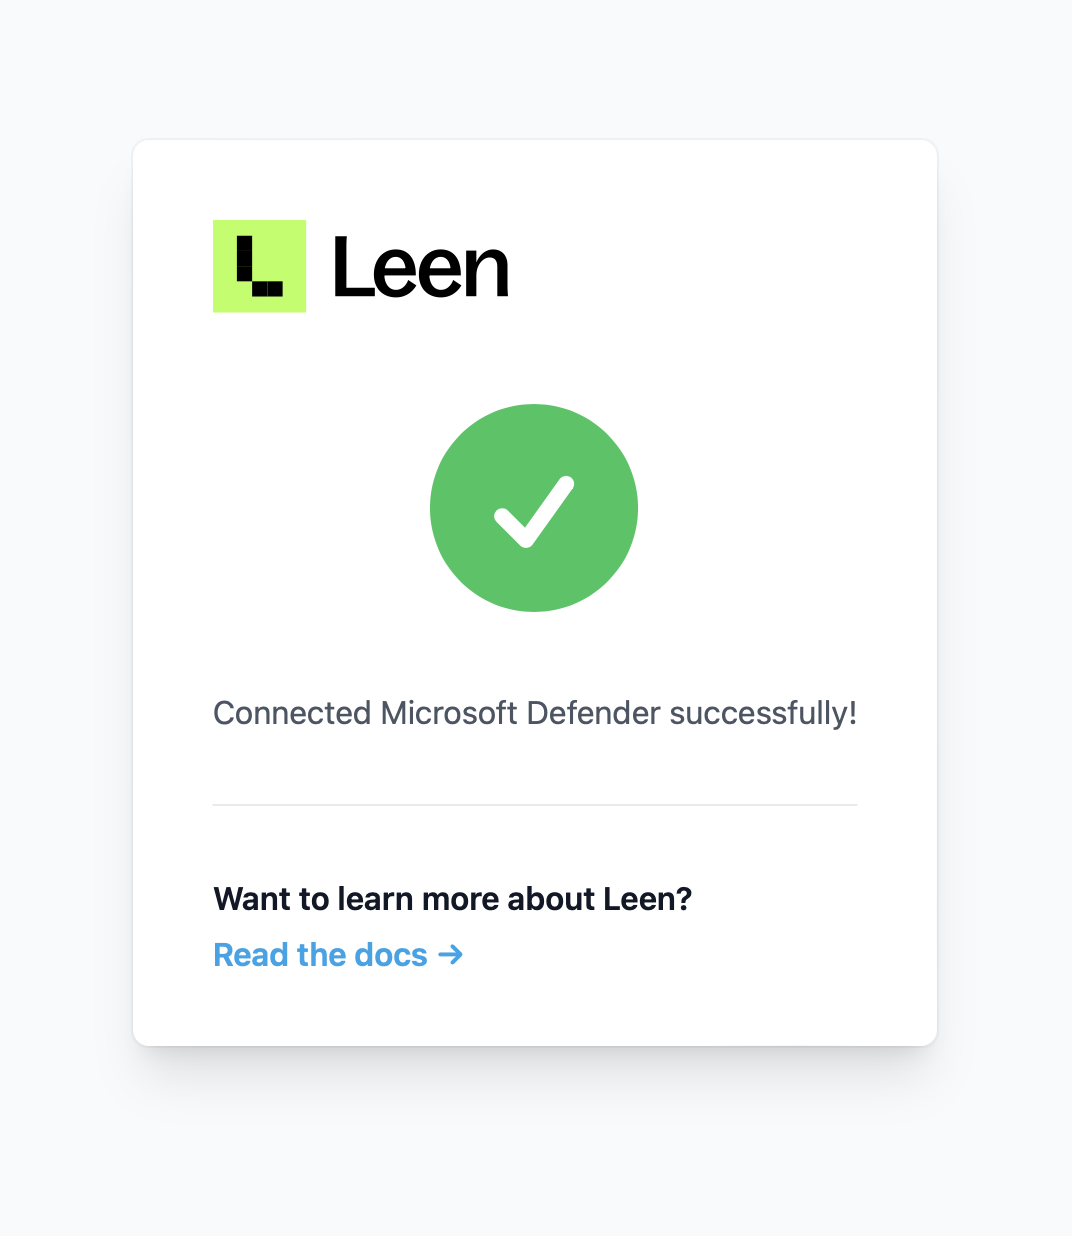 Now that the user has authorized the app, you can pull data from Microsoft Defender using the `connection_id` from the first step.
More information can be found on the [API Reference page.](/api-reference/idp/get-issues)
This documentation is built and hosted on [Mintlify](https://mintlify.com), a developer documentation platform.